Intro
Smart Phishing using the Ticket Feature of a Customer Support Software
I found a security vulnerability in Freshdesk that enables an attacker to send ticket requests via spoofing the sender. This vulnerability can be used in real-life scenarios to create smarter phishing attempts.
3rd Party Software - Help Desk
The ability to easily spoof an e-mail sender is always a great risk for organizations. Attackers hiding behind a trusted sender typically try to steal credentials from victims or hijack victims' computers with ransomware or other malware. To protect against such attacks, companies need security solutions to determine whether the sender of an e-mail is real. Inbound email filtering solutions used by companies can apply the company's email authentication service — using standards like SPF, DKIM, and DMARC — and quarantine emails that fail to meet those standards. With the effective implementation of such security measures, attackers develop interesting scenarios with new approaches.
Freshdesk is one of many Help Desk Softwares available for organizations to manage Customer Support Services.
Freshdesk, the online customer engagement solution from Freshworks, lets you streamline your company's customer support using the customer service software and helps you to efficiently manage your customers as you scale.
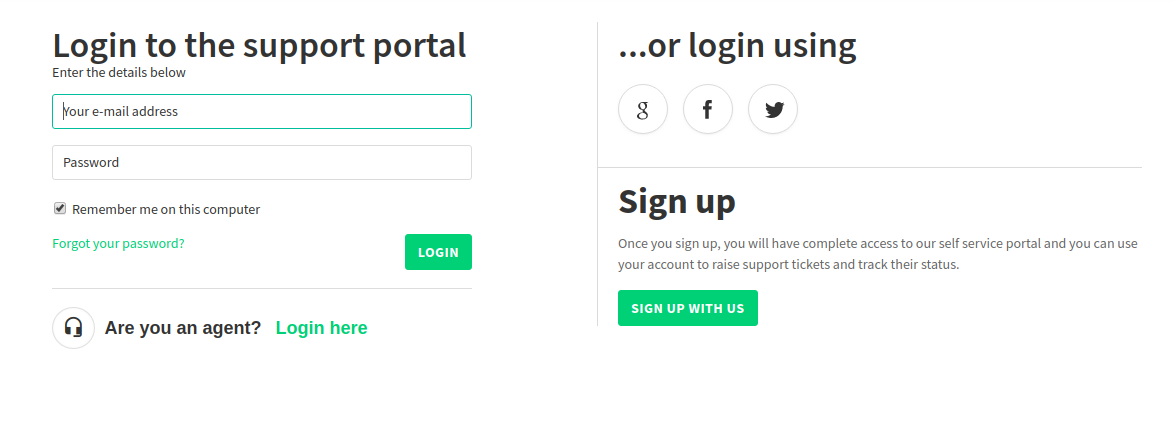
Freshdesk accounts can be accessed by default under companyname.freshdesk.com or support.company.com. Investigating the source code of the login page, strings like "Login to the support portal" or "Help Desk Software by Freshdesk" — the default Freshdesk title — are descriptive enough for attackers to use in a recon phase with a Google dork such as:
site:*.freshdesk.com intext:"Login to the support portal" OR "Help Desk Software by Freshdesk" -site:support.freshdesk.com
Freshdesk Vulnerability
Due to an authorization vulnerability caused by Freshdesk, an attacker can perform social engineering attacks by impersonating trusted sources.
Introduction
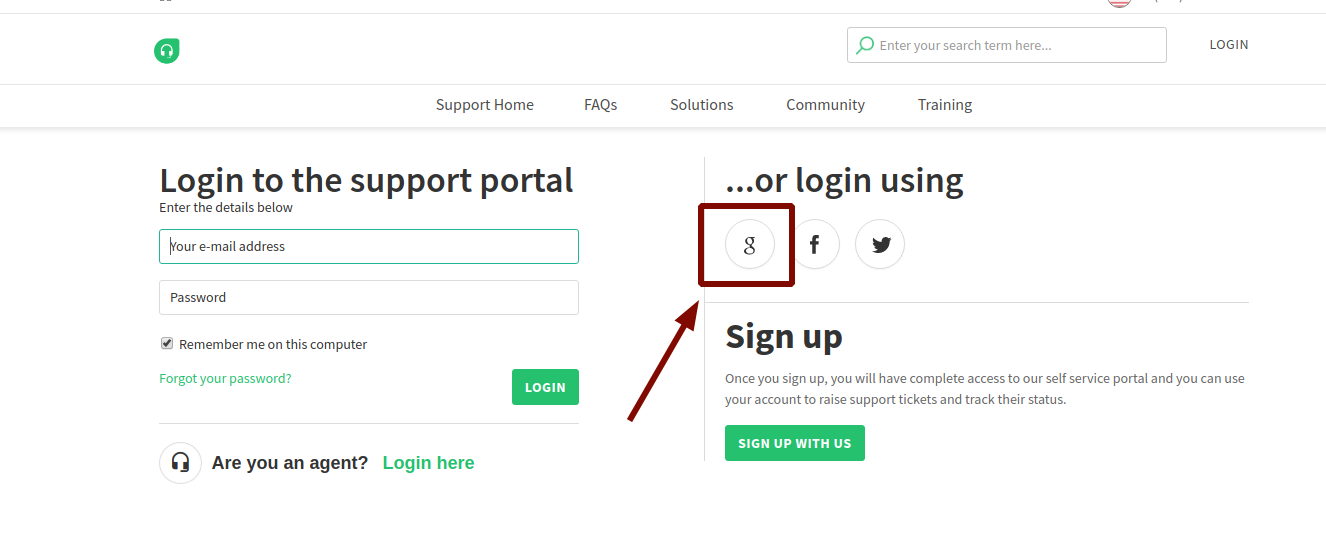
Support pages are not fully open to the outside. Login to the Freshdesk Support portal happens via one of:
- Social Accounts (Google, Twitter, Facebook)
- Signup Feature
Vulnerability Details
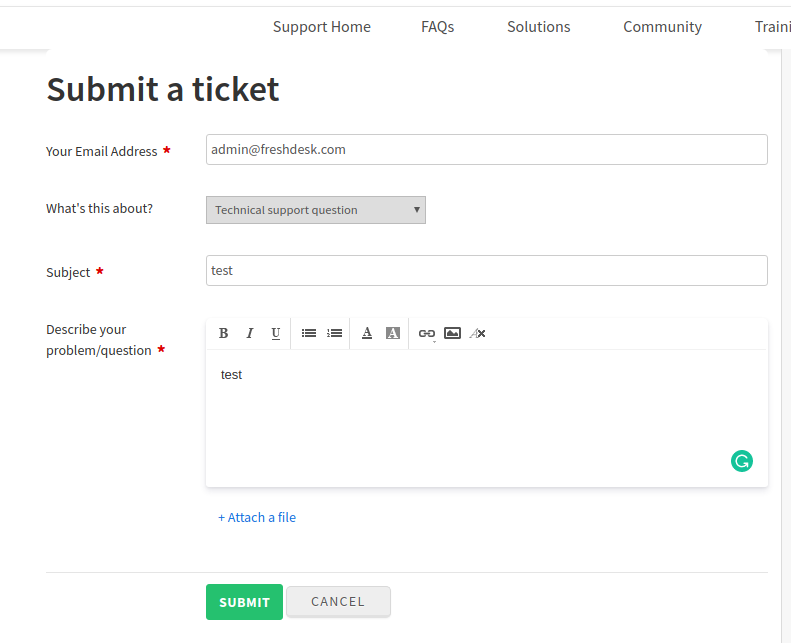
After logging in from a social account, access to the ticket submission page is granted. On this page, the "Sender email address" field can be changed by the end-user. Tests were planned in two ways: first with an email address that does not exist in the company, then with an actual company mailing address — identified beforehand through employee information on social networks such as LinkedIn.
Business relationship information includes the associates of a target and may be discovered via social media sites such as LinkedIn or public press releases announcing new partnerships between organizations or people. This information may be used by an adversary to shape social engineering attempts. (MITRE source: T1272)
When submitting a ticket using a spoofed sender address and clicking send, the browser is redirected to the login screen — at first glance suggesting the sender email is rejected due to an authorization check.
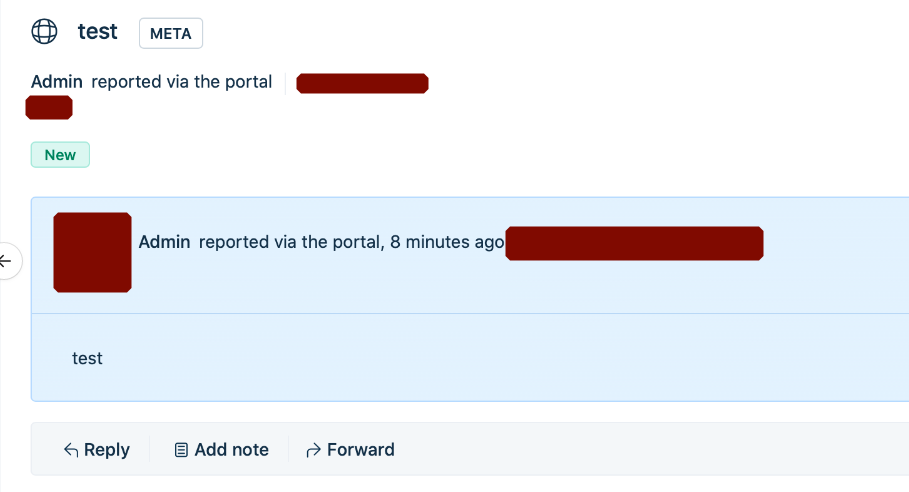
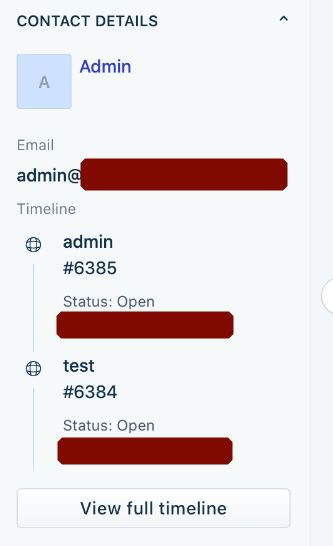
But checking the admin panel revealed that the tickets were created — under the spoofed sender addresses — despite the redirect to the login screen. This points to an authorization problem in how the ticket is actually processed versus how the redirect is displayed.
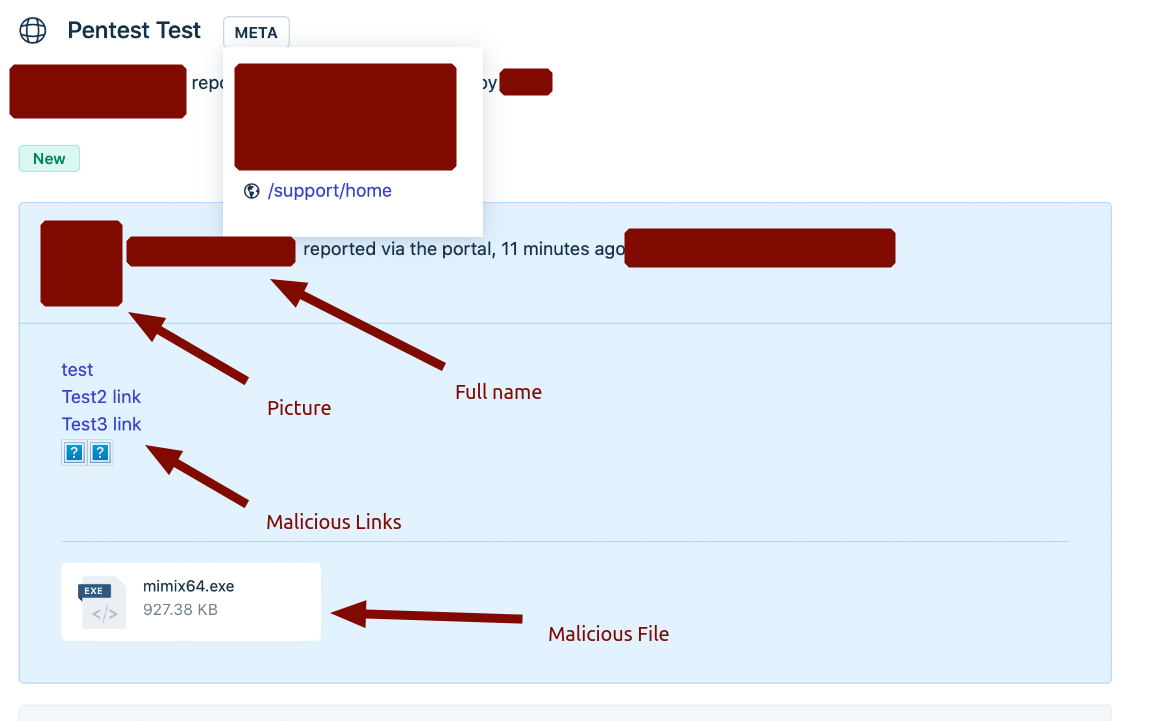
Examining the ticket in the admin panel further showed that an attacker could build a more realistic profile — using the target's surname and avatar — to imitate the sender's identity. With this information imitated, the resulting ticket format is quite convincing, and can be turned by attackers into a social engineering vector.
Impact
From an offensive perspective, this vulnerability's impact can be increased by combining it with the following lower-impact findings:
- An external link can be added to the message using the text editor, allowing a malicious website link to be added.
- Since the image HTML tag can be used in the editor, Net-NTLM can be hijacked for support employees on Windows machines.
- Since the form field includes a file-sending feature with no restriction on file extension, files with an
.exeextension can also be sent — allowing an attacker to deliver malware as an attachment.
Mitigation
The suggestion offered to Freshdesk: the sender's email address should not be changeable by the end-user.
The suggestion offered to organizations using Freshdesk: disable social login and/or verify registered users with a confirmation mechanism.
If social login is disabled completely, a message like the following is displayed instead:
Sorry! You do not have enough permission to access this page. Please contact your Account administrator.
Timeline
- April 14, 2020 — Discovered
- April 14, 2020 — Reported to Freshdesk Security
- April 14, 2020 — Closed as "Invalid" by Freshdesk
- June 3, 2020 — Public Disclosure
Special thanks to Barış Akkaya.