Introduction
Lolbas (Living Off The Land Binaries And Scripts) project was created by Oddvarmoe.
These are files provided by the operating system that are normally used for legitimate purposes but can be abused by malicious actors. Since these files are Microsoft-signed, they are considered to be trusted by organizations.
This project contains very useful features for Red teams. If a file or script has the following features, it can be considered as Lolbas:
- Executing code
- Compiling code
- File operations
- Persistence
- UAC bypass
- Credential theft
- Dumping process memory
- Surveillance (e.g., keylogger, network trace)
- Log evasion/modification
- DLL side-loading/hijacking
Analysis of Lolbas Files
Below is a brief analysis of the certutil, pester, pcwutl.dll, and zipfldr.dll files from the existing Lolbas techniques. Additionally, some information is shared that can support researchers in discovering new Lolbas techniques.
Certutil.exe
Certutil.exe is a command-line program that is installed as part of Certificate Services. You can use Certutil.exe to dump and display certification authority (CA) configuration information, configure Certificate Services, back up and restore CA components, and verify certificates, key pairs, and certificate chains.
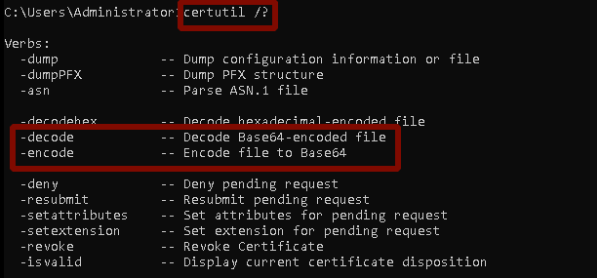
In order to understand how a program works, it is important to understand what parameters can be given as input. Checking the input parameters of certutil.exe with /? or /help gives preliminary information for further investigation.
/? shows that certutil.exe can be used for encoding plain-text data with the base64 algorithm. Attackers use this feature to evade security measures.
Pester.bat
Pester is a test framework for PowerShell. It provides a language that allows you to define test cases and the Invoke-Pester cmdlet to execute these tests and report the results.
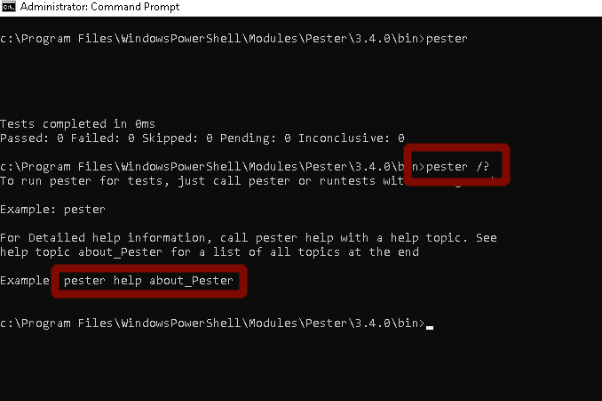
Examining the pester.bat file used by PowerShell: after using the pester /? command, the help and about_Pester arguments appear.
Analyzing the source code of pester.bat shows that the %2 variable (related to about_pester) can be controlled by the attacker.
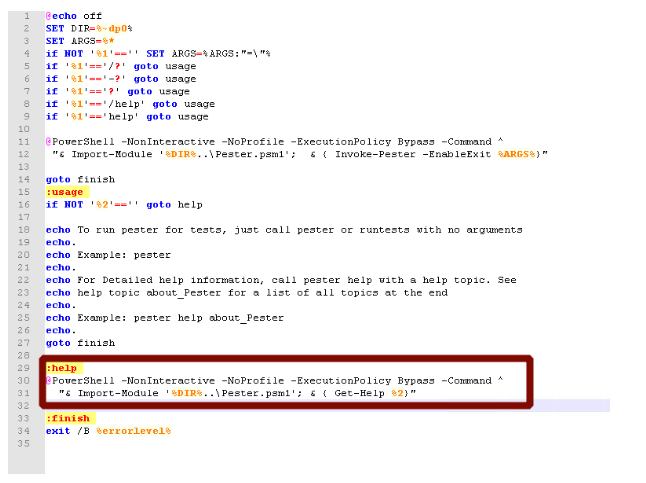
The attacker can inject malicious commands using this part:
pester.bat help "$null; calc"
pester.bat /help "$null; calc"
pester.bat ? "$null; calc"
pester.bat -? "$null; calc"
pester.bat /? "$null; calc"
Pester.bat Lolbas technique
Lolbas DLL Files
Some Lolbas DLL files are worth analyzing. Executing rundll32.exe pcwutl.dll, LaunchApplication calc.exe calls the LaunchApplication function from pcwutl.dll (the Program Compatibility Wizard Utility DLL) via Rundll32.exe. The LaunchApplication function executes its parameter and spawns the calc.exe application.
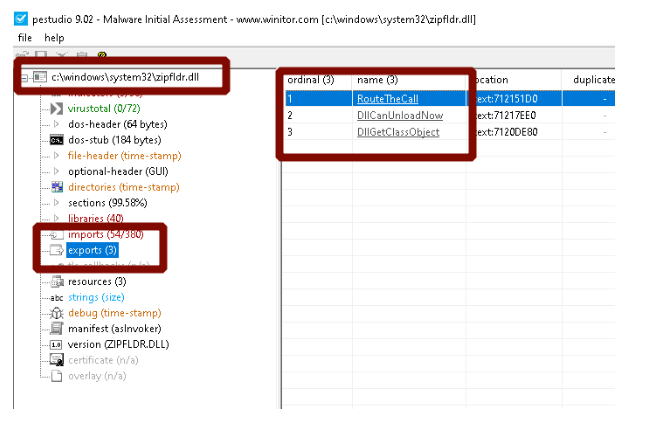
In another DLL example, calc.exe was executed the same way by calling the RouteTheCall function with rundll32.exe zipfldr.dll, RouteTheCall calc.exe.
At this point, exported functions of system DLLs can be analyzed. Using the Pestudio tool, the relevant function information of a DLL file can be found in the Export menu.
Lolbas - Blind Points
For programs that do not give output when the help command is used, the following methods can be applied:
- Search the relevant help documents (for instance, Microsoft commands).
- Try to execute it on older operating systems such as Windows 7.
- Inspect with tools such as Strings, IDA.
- Fuzz certain parameters — for instance, calling calc.exe for
[a-z]parameters.
Pcalua.exe is the Program Compatibility Assistant. "The Program Compatibility Assistant is an automatic feature of Windows that runs when it detects an older program has a compatibility problem."
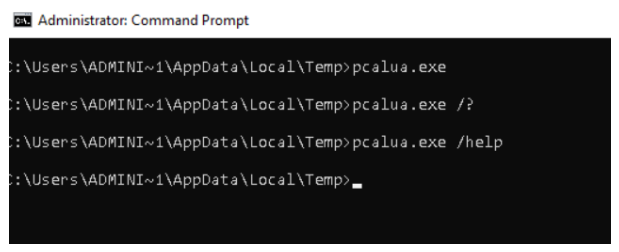
Calling the help menu of the pcalua.exe file gives no result on a Windows 10 machine. A simple Google search revealed the -a parameter, used on Windows 7. Calling pcalua.exe -a calc.exe executes the calculator.
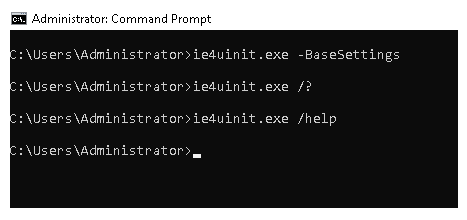
The genuine ie4uinit.exe file is a software component of Internet Explorer by Microsoft Corporation. "Ie4uinit.exe" is a Microsoft utility program having both 32-bit and 64-bit versions.
The ie4uinit.exe file in the Lolbas project has a -BaseSettings parameter. Standard help parameters return no information about the command.
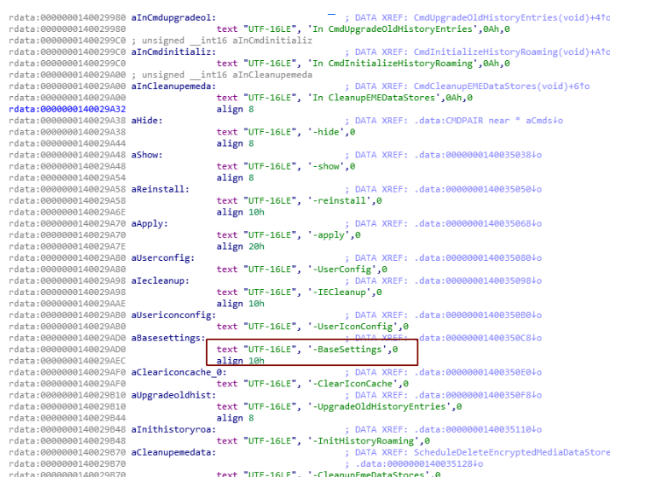
Using IDA's "text search" feature to find other parameters besides -BaseSettings reveals different parameters such as -hide, -show, etc.
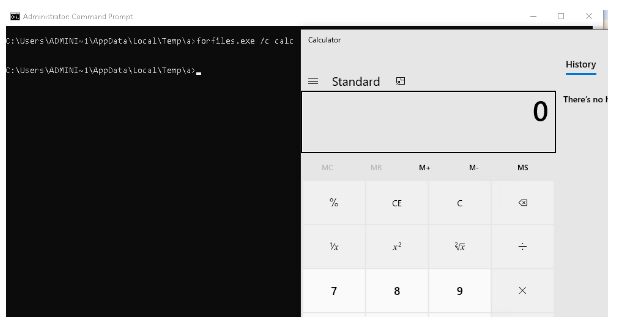
Forfiles is a useful Windows command to select a set of files and then run a command on each of the files. It's similar to the functionality of the find command on Linux OS.
Examining the parameter list of the forfiles.exe command shows it can take input parameters like p, m, and c:
forfiles /p c:\windows\system32 /m notepad.exe /c calc.exe
Reading the help output further shows calc.exe can be executed using only the "c" parameter:
forfiles.exe /c calc.exe
Non-Microsoft Lolbas
The Lolbas project includes Microsoft-signed files that exist in the operating system. As a different approach, Lolbas-style behavior can also be found in programs belonging to organizations other than Microsoft. To explore this, the desktop application Notion (notion.so) — a note-taking application used by over 1M people — was analyzed.
Using the Procmon tool while examining the desktop application gives an idea of the files created by the Notion desktop application, filtered by the installer's process name and the CreateFile operation.
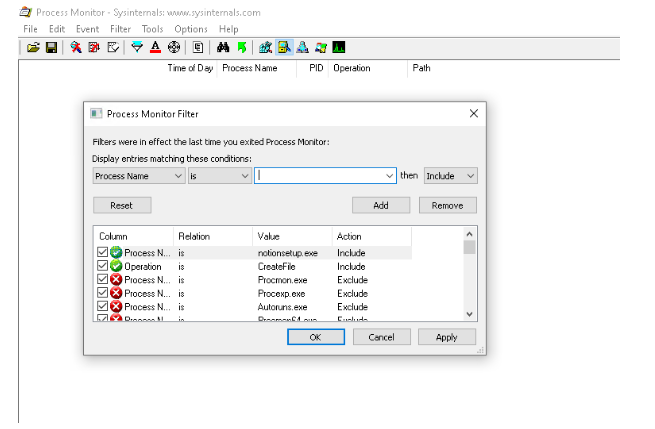
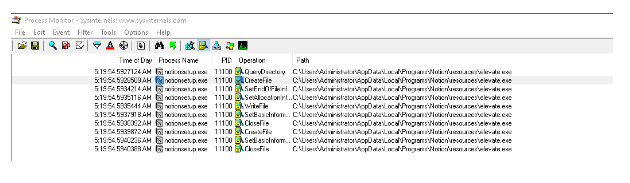
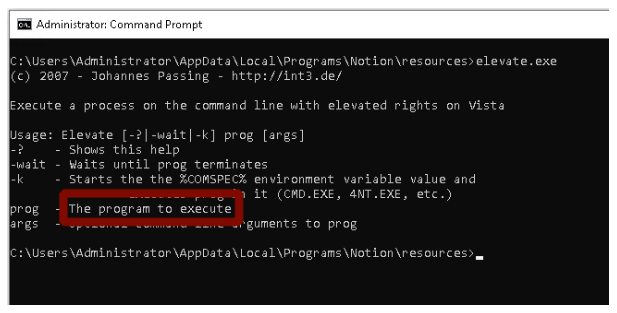
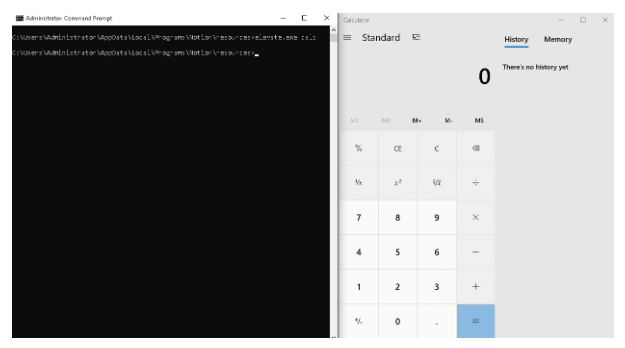
The installer creates a file called elevate.exe (a tool written by Johannes Passing) in C:\Users\Administrator\AppData\Local\Programs\Notion\resources. By sending a command to this program, calc.exe can be executed. Since another program can be called using the elevate program, this program can be considered a Lolbin.
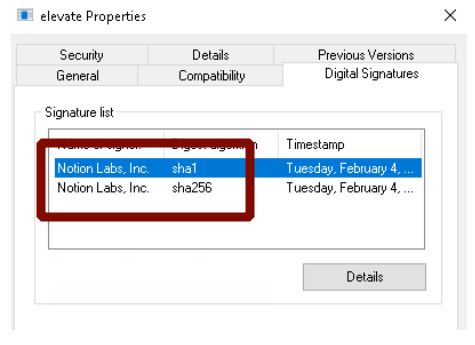
The digital signature of this tool shows that it was signed by the company Notion.
Conclusion
Attacks using LOLBins seem to be increasing. Multiple ways to manipulate these files are constantly shared, so creative defense strategies need to be implemented in the systems.
References
- https://medium.com/@mattharr0ey/lolbas-blowing-in-the-binaries-path-c480176cc636
- https://notoriousrebel.space/2019-07-13-automating-the-hunt-for-lolbas/
- http://www.hexacorn.com/blog/2019/07/05/bring-your-own-lolbas/
- https://www.microsoft.com/security/blog/2019/09/26/bring-your-own-lolbin-multi-stage-fileless-nodersok-campaign-delivers-rare-node-js-based-malware/
- https://blog.talosintelligence.com/2019/11/hunting-for-lolbins.html
- https://liberty-shell.com/sec/2018/10/20/living-off-the-land/
- https://stackoverflow.com/questions/8869219/how-can-i-find-out-if-an-exe-has-command-line-options
- https://github.com/LOLBAS-Project
Thanks to Barış Akkaya.